How FCI protects your data, your decisions, and your records
We hold an accredited quality system under ISO/IEC 17025:2017, are actively pursuing CMMC Level 2 (for DoD work) and SOC 2 Type II (for commercial data-handling), and apply security controls aligned with both frameworks today.
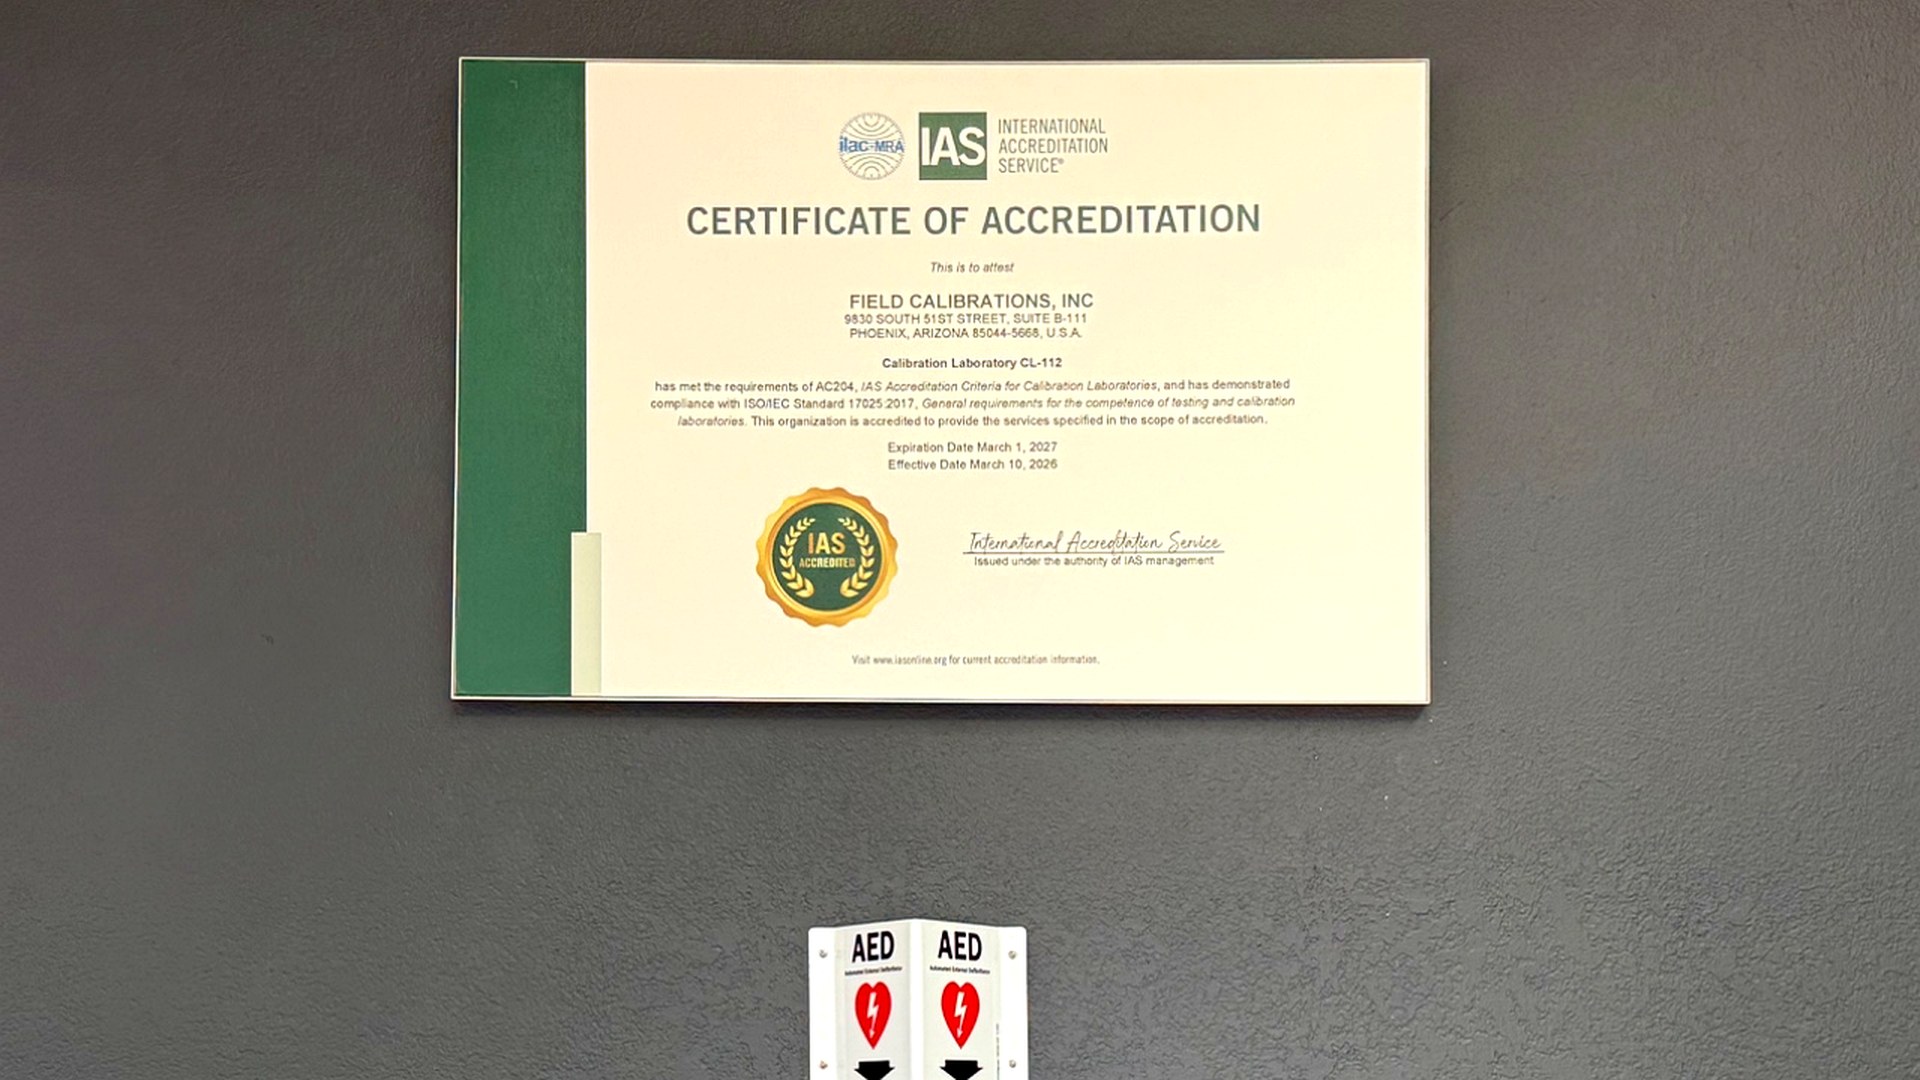
ISO/IEC 17025:2017 — IAS CL-112
FCI is accredited by the International Accreditation Service (IAS) under accreditation number CL-112. Accreditation covers our entire scope of calibration and the supporting quality management system.
What ISO/IEC 17025 covers for you
- · Documented technical competence of laboratory staff
- · Controlled procedures for every measurement parameter
- · Documented measurement-uncertainty budgets at every test point
- · Unbroken NIST traceability with documented chains
- · Formal nonconforming-work, complaint, and corrective-action procedures
- · Independent surveillance audits by IAS on a recurring cadence
What we can share
- · Current IAS CL-112 accreditation certificate
- · Full 21-page IAS scope of accreditation (parameter ranges + uncertainties)
- · Alignment one-pager (AS9100, ISO 13485, IATF 16949, AMS 2750, ANSI/NCSL Z540)
- · W-9 and vendor-details one-pager
- · QA-SOP-001 Complaint Handling Procedure (ISO/IEC 17025 §7.9)
Request the complete package via Supplier Qualification.
Controls in place today
These are the technical and administrative controls FCI applies today. They are organized to map directly onto CMMC Level 2 (NIST SP 800-171) practice families and SOC 2 Common Criteria.
Access control
Microsoft 365 with conditional access, MFA on all administrative accounts, role-based access to QuickBooks, MET/TEAM, and shared file storage. Quarterly access review.
Audit & accountability
Centralized log retention for application, server, and email; honeypot anti-bot, request-rate limiting, body-size caps, and admin-action audit trail.
Configuration mgmt
Trust-proxy, HSTS, CSP, X-Frame-Options DENY, X-Content-Type nosniff, Referrer-Policy, Permissions-Policy, and Cross-Origin policies enforced sitewide.
Identification & auth
MFA across all M365 accounts, no-reply outbound from a non-monitored mailbox, constant-time admin password compare, environment-variable credentials only — never in source.
System & comms protection
TLS-only transport (HSTS preload), upgrade-insecure-requests, locked-down CSP, no third-party trackers, no inline data exfiltration vectors.
Incident response
Formal ISO/IEC 17025 §7.9 complaint procedure with independent reviewer per §7.9.7, documented escalation paths, and management review of all classified incidents.
Inherited platform controls
Beyond the technical controls we operate ourselves, our website infrastructure inherits SOC 2 Type II and ISO 27001:2022 assurance from independently audited service providers.
SOC 2 Type II
Vercel (web hosting) and GitHub (source control) both hold SOC 2 Type II attestations for Security, Availability, and Confidentiality. FCI’s public website inherits platform-layer controls under each provider’s shared responsibility model.
Verify at Vercel Trust Center →ISO/IEC 27001:2022
Vercel and GitHub are both ISO 27001:2022 certified, covering their Information Security Management Systems. FCI’s site infrastructure runs on this ISMS-certified stack.
Verify at Vercel Trust Center →CMMC Level 2 and SOC 2 Type II
FCI is pursuing two formal certifications to broaden federal eligibility and meet commercial-aerospace and medical-device data-handling expectations.
CMMC Level 2 (NIST SP 800-171)
For DoD work involving Controlled Unclassified Information (CUI). FCI maintains a current SPRS score and a System Security Plan (SSP) aligned to NIST SP 800-171 Rev. 2. We do not currently process CUI; certification readiness is being built in parallel with our federal-capture pipeline.
Target: Level 2 self-assessment in advance of DoD work; third-party certification (C3PAO) as warranted by contract requirements.
SOC 2 Type II (Security & Availability)
For commercial-aerospace, medical-device, and semiconductor customers whose supplier-qualification programs ask about data-handling controls. We will pursue SOC 2 Type II covering Security and Availability Trust Service Criteria as part of our 2027 roadmap.
Target: Type I observation period H1 2027; Type II audit window H2 2027.
Privacy Policy
Plain-language summary of how we handle the information you submit through this website.
What we collect. When you submit a quote, certificate, supplier, feedback, complaint, reminder, contact, careers, or CalStudio portal-notify form, we collect the fields you fill in plus a server timestamp and your IP for abuse prevention. Career applications also accept resume + cover letter PDFs you choose to upload.
How we use it. Form submissions route to the responsible FCI inbox for that workflow (sales, quality, HR, contact, etc.) so we can respond. We store submissions in a controlled-access database for audit and recordkeeping. We do not sell, rent, or share your submissions with third parties for marketing.
Who sees it inside FCI. Only the staff with a need-to-know for that workflow. Customer-feedback and complaint forms are reviewed at executive level per our ISO/IEC 17025 §7.9 program.
Cookies. This site sets only the cookies strictly necessary to make the site work (theme preference, session). We do not use third-party tracking or advertising cookies.
Email. All automated outbound email comes from no-reply@fieldcal.com, an unmonitored mailbox. Replies should go to info@fieldcal.com or the address from which a real person responded.
Retention. Quality records (calibration certificates, complaints, corrective actions) are retained per ISO/IEC 17025 retention requirements. Career applications are retained per FCI HR policy. Marketing-form submissions are retained no longer than necessary for the workflow.
Your rights. Email info@fieldcal.com to request access, correction, or deletion of personal information you submitted. We will respond within a reasonable timeframe consistent with our recordkeeping obligations.
Contact. Privacy questions: info@fieldcal.com. Security issues: same.
Terms of Use
Brief terms governing your use of this website.
Use of this website. This site is operated by Field Calibrations, Inc. for informational and customer-service purposes. Content may be downloaded for legitimate evaluation, audit, or supplier-qualification purposes. Bulk scraping, reverse engineering of forms, or automated abuse is prohibited.
No warranty. The content on this website is provided "as is" without warranty. Calibration is delivered under the certificate and accreditation conditions of the actual service engagement — not the website.
Capability claims. Anything on this site framed as "in progress," "in pursuit," or "planned" is precisely that; FCI does not claim certifications it has not yet earned. The current accreditation is ISO/IEC 17025:2017 by IAS (CL-112).
Governing law. Disputes arising from use of this site are governed by the laws of the State of Arizona, USA.